
Use any AI. Leak nothing.
AI data protection for people, apps and agents.
See which AI apps your company uses, coach people when they're about to share too much, and mask names, card numbers, IBANs and API keys before they reach any AI model. Your people keep using ChatGPT, Copilot and Claude, and the providers never see the data. For your own apps, the real values can go back in the answer.
28-day free trial or 10,000 requests, whichever comes first · no card needed
Where personal data and AI use need a clear boundary
Financial servicesInsuranceHealthcareLegalSaaS & techPublic sectorUse any AI model
with your data masked
What the employee types, and what the AI provider receives
What the employee types
Draft a reply to Ada Lovelace about her
refund of CHF 2,400 to card
4532 7781 0021 9047
IBAN CH93 0076 2011 6238 5295 7
What the AI provider receives
Draft a reply to mf_mask_170b about her
refund of mf_mask_9c2e to card
mf_mask_41af
IBAN mf_mask_d7e0
574 detectors · 47 country packs · 7 AI apps · 9 AI providers · prompts and answers never stored
Sound familiar?
The usual answers either leak data or stop the work.
“We banned ChatGPT.”
“Our DLP blocks it.”
“We'll redact it in the app.”
What Maskflare does
Discover AI use, guide people, and keep sensitive data out of every model.
Discover and control AI apps
See which AI apps people use, with a risk score per app. Tell company accounts from personal ones. Approving, tolerating or blocking apps is in beta.
Learn moreCoach users in the moment
Beta
Warn and ask for a reason instead of a silent block. Your message, your AI policy link, and feedback that tunes rules.
Learn moreMask prompts, check files and answers
Personal data and secrets are masked in 7 AI web apps before they reach the provider. Uploads are scanned or refused, and answers in ChatGPT and claude.ai are read for alerts, not rewritten.
Learn moreProtect your own AI apps
One base-URL change puts the gateway in front of 9 AI providers, with streaming, embeddings and SDKs.
Learn moreSecure coding agents and MCP
Hooks for Claude Code, OpenAI Codex, Cursor, GitHub Copilot CLI and VS Code agent mode, MCP masking, prompt-injection detection, and MCP access control per group (beta).
Learn moreIdentity, policy and SIEM
Single sign-on and SCIM provisioning with Microsoft Entra ID, Okta and Google Workspace, four-eyes approval and events to your SIEM. Per-group policies are in beta.
Learn moreCompliance profiles
One-click rule sets for HIPAA Safe Harbor, GDPR (EU/EEA), UK GDPR, PCI DSS v4.0, US PII (CCPA/CPRA) and Swiss nDSG health data, with coverage reports you can hand to an auditor.
Learn moreSee it on your own data
Start a trial, send your own prompts through it, and see what was masked and why.
Start free trial- AI apps
- ChatGPT, Claude, Gemini, DeepSeek, Perplexity, Mistral Le Chat and Microsoft 365 Copilot
- AI providers
- OpenAI, Anthropic, Google Gemini, Mistral, xAI, DeepSeek, Groq, Together AI and Ollama
- Coding agents
- Claude Code, OpenAI Codex, Cursor, GitHub Copilot CLI and VS Code agent mode
- Device management
- Microsoft Intune, Jamf, Group Policy
- Identity
- Microsoft Entra ID, Okta and Google Workspace
574
built-in detectors47
country packs, checksum-validated100%
of 708 values found in our 228-case Swiss benchmark, 0 false positives~2 ms
median added per 10 KB request on default rules
Benchmark and latency figures come from Maskflare's own test sets; latency is measured before the named-entity layer.
One policy, three ways in
Every way in.
One policy.
Company data reaches AI models through three doors. Most tools watch one. Maskflare puts the same rules on all three, so a card number gets the same treatment whether a developer, an employee or an agent sends it.
- Door 01
Your apps
Point your OpenAI or Anthropic client at the Maskflare gateway: one base-URL change. Or call the Python and TypeScript SDKs directly. Streaming works, and real values come back in the answer.
Gateway and SDKs - Door 02
Your people
IT rolls out the desktop agent through Intune, Jamf or Group Policy. It shows which AI apps are in use, coaches people at the moment of a risky paste, and masks prompts and readable text uploads in ChatGPT, Claude, Gemini, DeepSeek, Perplexity, Mistral Le Chat and Microsoft 365 Copilot before they reach the provider.
Workforce desktop agent - Door 03
Your agents
Tool calls to MCP servers are masked in both directions and governed per group. Claude Code, OpenAI Codex, Cursor, GitHub Copilot CLI and VS Code agent mode get hooks that stop a pasted secret before it reaches the model.
Agent & MCP security
Maskflare · one policy under every path
Detect
574 detectors, checksums, your own records
Mask and restore
Reversible tokens, kept 30 days
Policy and approvals
Per environment, four-eyes changes
Audit
Metadata and counts, never prompts
The Maskflare platform
Less exposure.
More possibility.
Connect your people, applications, and AI workflows with a layer of protection. Keep the context your business needs. Control the data it shares.
Popular guides
- // 01 original request
- Help Alex Morgan with their order. Send an update to alex@example.com.
- // 02 masked for AI
- Help [PERSON_1] with their order. Send an update to [EMAIL_1].
- // 03 restored on API traffic, inside your boundary
- Alex Morgan, we’re looking into your order. We’ll send an update to alex@example.com.
Illustrative workflow using synthetic data. Readable labels stand in for the opaque tokens Maskflare actually sends. Step 03 applies to API traffic with restoring on. In AI web apps the answer isn't rewritten, so a token the model repeats stays a token.
Product tour
Click through the console
Five screens, no signup. These come from a demo organization, and all the people, devices and numbers are made up.
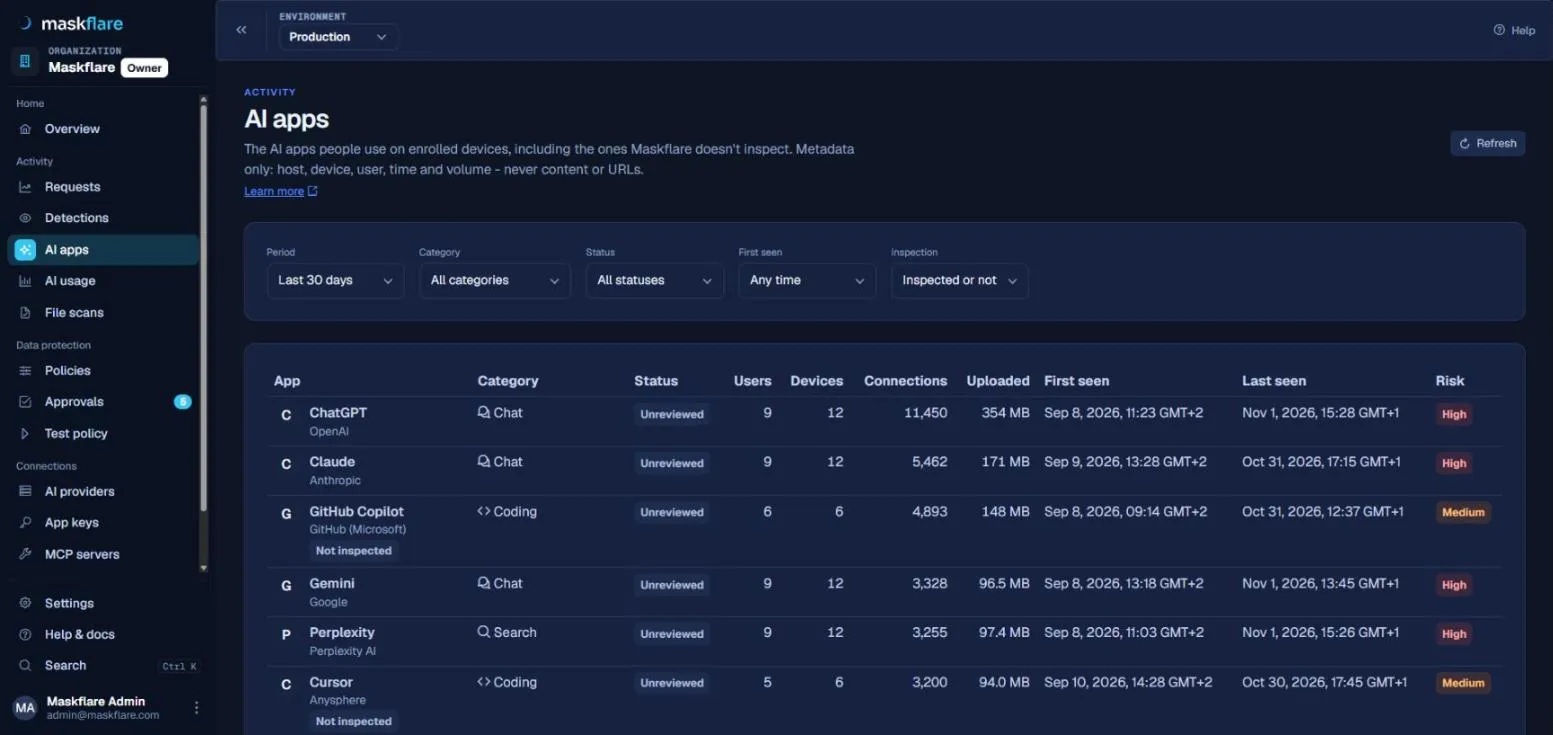
See which AI apps people actually use
The AI apps page lists what's in use on enrolled devices, with users, devices, volume and a risk rating. It records metadata only, never what was typed.
Built for real company data
Not demos.
Real traffic.
The same engine sits behind the gateway, the SDKs, the desktop agent and MCP masking. EU-hosted by default, with on-premises deployment for enterprises.
How detection works01
Checks, not guesses
National IDs, IBANs and card numbers are validated with their checksums or format rules across 47 country packs, so a random order number isn't flagged as a Visa card. Same input, same result, every time.
Detection engine02
Your own records
Upload your customer list as keyed hashes with Exact Data Match. Any exact match in a prompt is masked; the clear values never leave your environment.
Exact Data Match03
Files too
Documents are text-scanned in a sandbox, images lose their GPS and camera metadata, and plain-text uploads are masked in place.
File security04
Audit, never the prompt
Who used which model and what was masked: metadata and counts only. About 2 ms added to a typical chat request with the default rules.
Admin consoleBefore you start a pilot
The questions security teams ask us first.
Short, direct answers. The trust center covers data handling, hosting and our audit status in more detail, and we're happy to go through your security questionnaire.
Frequently asked questions
Isn't this just regex?
No. Identifiers are matched with patterns and then checked: 108 validators (checksums and format rules) for IBANs, cards and national IDs, context words, and negative context that rules out order and invoice numbers. A local named-entity layer finds names, places and free-text details. Every match is explained in the console.
Why not Microsoft Purview?
Purview governs what Copilot can read inside Microsoft 365. Maskflare masks what people and apps send to any AI model, Copilot included, and on API traffic from your own apps it can restore the values in the answer. Many teams use both.
How is Maskflare different from Harmonic Security or Nightfall?
Both can warn, block or redact. Maskflare is built around reversible masking: the prompt goes through with personal data replaced by tokens. On API traffic the real values can come back in the answer; in AI web apps the answer isn't rewritten, so a token the model repeats stays a token. It keeps no copy of prompts, and the same rules cover your own AI apps through a gateway as well as employees.
Can't we just block ChatGPT?
Blocking moves usage to phones and personal accounts, where you see nothing. Approve one assistant, block personal accounts and risky apps, mask sensitive data, and coach people with warn-and-justify prompts.
Does masking break the AI's answers?
No. Each value becomes a consistent token, so the model can still reason about it, and Maskflare puts the real value back wherever the answer repeats it, including while the answer streams.
Does Maskflare store our prompts?
No. Prompts, answers and files pass through and are never logged. To restore values in answers, the original values are kept encrypted for 30 days, then they expire. Customer data is never used to train AI models.
Where is it hosted?
In the EU by default. Enterprises that need it can run Maskflare on-premises, so unmasked data never leaves their own infrastructure.
Is this employee surveillance?
No. Discovery records which AI app was used and how much was uploaded, never what was typed or which sites people visit, and names can be hidden behind departments.
How long does rollout take?
A developer can route a first request through the gateway in minutes. A device pilot starts with a handful of laptops in monitor mode, rolled out with Intune, Jamf or Group Policy on Windows, macOS and Linux.
Are you SOC 2 or ISO 27001 certified?
Our SOC 2 Type II and ISO 27001 audits are in progress. During evaluation we share our security documentation, data processing agreement and sub-processor list.
Does it help with GDPR, the Swiss nDSG and the EU AI Act?
It's a technical measure for data minimization and transfers under GDPR and the nDSG, with compliance profiles for HIPAA Safe Harbor, GDPR (EU/EEA), UK GDPR, PCI DSS v4.0, US PII (CCPA/CPRA) and Swiss nDSG health data. For the EU AI Act, the AI app inventory supports AI literacy and risk work. No tool makes you compliant on its own.
Learn and compare
Clarity comes first.
Keep personal data out of your LLM calls.
Code-first guides for OpenAI, Anthropic, Gemini and LiteLLM, with Python and TypeScript examples.
Read the guidesGDPR and AIIs ChatGPT GDPR compliant?
What changes between free and business plans, what GDPR asks of you, and a practical setup for EU and UK companies.
Read the articleSee it on your own data
Try Maskflare free.
Bring your hardest prompts.
28-day free trial or 10,000 requests, whichever comes first. Point one app at the gateway or enroll a few laptops, and watch what gets masked. Or talk to us first.
- SOC 2 Type II: In progress
- ISO 27001: In progress
- EU hosting by default · on-premises available
- Prompts and files never stored
- Never used to train AI models
- GDPR · nDSG · DPA available
- Trust center